Meta states that Muse's conversations and virtual machine data are not shared with its advertising systems, but its own technical security document clarifies that this protection is operational policy, not a cryptographic barrier, and Muse's App Store privacy label explicitly lists "third-party advertising" among the purposes for which data like health, financial information, location, contacts, and browsing history linked to the user are used. Two weeks after Muse launched on September 8, 2026, Meta reached a settlement of up to 17.1 billion dollars with 29 state attorneys general over child safety claims, a trust context any business should know about before deciding how much client information flows through this tool.
We already covered what Muse is and what it means for an AI agent to complete purchases on a consumer's behalf on launch day itself. This second piece specifically reviews what the terms of service and privacy policy say about using data for marketing, and what the first week of real reactions revealed that the launch announcement didn't tell you.
What does Meta officially say about using Muse data for advertising?
Meta directly states that Muse's conversations and data generated inside its secure virtual machine are not shared with the company's advertising systems, and that users can opt out of having their interaction data used to train future Meta AI models. The technical architecture includes a separate agent called Sentinel, which runs on the same virtual machine but is kept isolated from Muse at the system level, and which must approve any information before it leaves toward the internet.
Meta also states that user credentials stay hidden from Muse, that sensitive actions require explicit approval, and that service access can be revoked at any time. According to eesel AI, which reviewed the product in its first week, there is no advertising inside Muse currently, though the company is exploring commerce revenue, confirming Meta has active commercial intent around this product beyond offering it as a free assistant.
Why doesn't the App Store privacy label fully match that message?
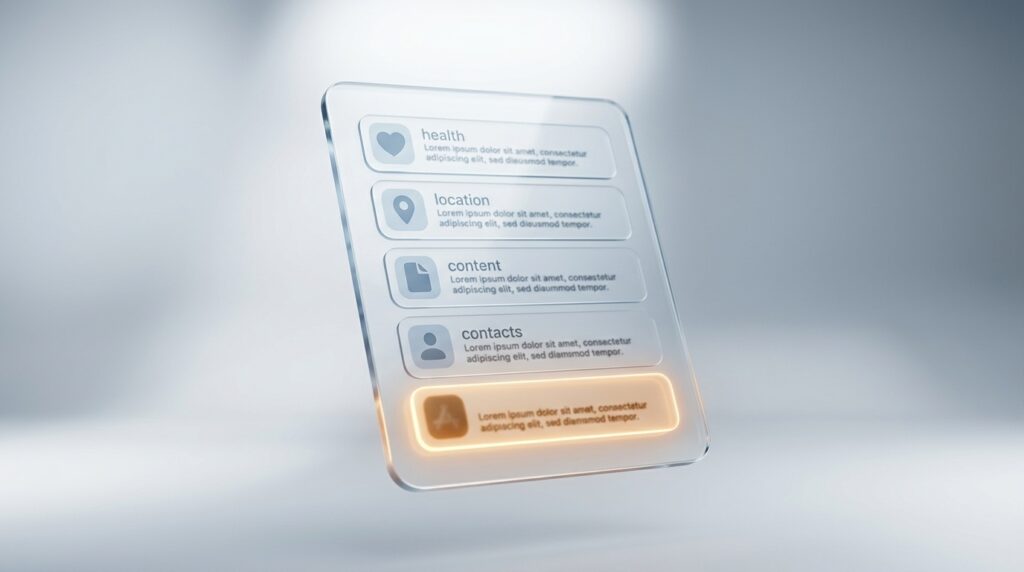
Muse's App Store privacy label, a mandatory legal disclosure document, not a marketing communication piece, lists health and fitness, financial information, location, contacts, user content, and browsing history as data linked to the user's identity, with "third-party advertising" explicitly named among the purposes of use. This is a distinct and more reliable source than Meta's press announcement, precisely because Apple requires these labels to reflect legal accuracy about how data is used, not how the company prefers to describe it.
This discrepancy does not necessarily mean Meta is lying in its launch announcement. It is entirely possible for both statements to be true at the same time: that Muse's specific conversations do not directly feed advertising systems, and that the app as a whole does collect and use broad data categories for third-party advertising through other channels. For any business evaluating this tool, the legal App Store label is the source worth reviewing directly, not just the privacy message that appears in launch materials.
What does it mean that current protection is "policy, not cryptography"?
Meta's own technical security document clarifies that Muse's current architecture does not prevent Meta from accessing data when necessary to support, secure, or operate the service, meaning today's privacy protection depends on Meta following its own internal rules, not on a technical barrier that makes that access impossible even if the company wanted it. The difference is exactly what separates a promise from a guarantee.
The solution that would offer a real technical barrier, called Muse Confidential VM, is a hardware-encrypted environment with a cryptographic key only the user holds, specifically designed to prevent Meta's own personnel from accessing the data. Meta hired Moxie Marlinspike, Signal's founder, to build it, a signal the company is taking the problem seriously. But this feature was announced as coming "later this year," with no confirmed date. Until that arrives, any decision to trust sensitive information to Muse rests on Meta's operational policy, not on a technical impossibility of access.
How can Muse's activity indirectly influence advertising?
Even though virtual machine data and conversations are not directly shared with Meta's advertising systems, activity Muse performs on external websites or services can indirectly affect advertising, as the company itself acknowledges. There is a simple explanation for this: when Muse browses, buys, or fills out a form on an external site using its built-in browser, that visit can trigger the same advertising tracking mechanisms (cookies, pixels, retargeting technologies) that would trigger if a human had done exactly the same thing from their own browser.
For an advertiser, this has a direct practical implication: the fact that Muse is completing the transaction does not take it out of the normal advertising tracking ecosystem of the site it visits. If your page has a conversion pixel installed, it is reasonable to expect that pixel to still fire when the visitor is an AI agent acting on a person's behalf, exactly as we documented when analyzing what it means for an AI agent, not a person, to complete your checkout in our first Muse analysis. The difference between Muse and a human browsing your site, from the perspective of your own measurement system, may be smaller than it first appears.
What changed in the trust context two weeks after launch?
On September 8, 2026, Meta launched Muse. Roughly two weeks later, the company agreed to pay up to 17.1 billion dollars to resolve claims from 29 state attorneys general related to child safety, adding to an earlier lawsuit in New Mexico where Meta was ordered to pay 942 million dollars in damages related to minors. Neither of these cases is directly related to Muse as a product, but both are part of the same company track record any business should weigh before deciding how much trust to place in its privacy guarantees for a new product.
TechCrunch summed it up directly in its launch coverage: the real question is not whether Meta's security documentation sounds solid on paper, it is whether the company has enough accumulated consumer trust for an agent like this to succeed, given that Meta has a history of proclaiming one thing and doing another. That is not our opinion, it is the assessment of one of the most established tech outlets, published the same day as the launch.
This same pattern of looking more carefully at what happens after a launch's initial hype is exactly what we applied when analyzing GPT-6 Astra one week after its own launch:: the real evidence almost always arrives later, more nuanced, and more useful than the first day's announcement, no matter which AI company is behind the product.
What does the real first week reaction say?
Early hands-on tests highlighted speed as Muse's standout trait, with Muse Spark 1.3 running past 200 tokens per second without the chat feeling slow, backed by a generous free limit of 100 million tokens per week announced by Mark Zuckerberg himself. But the same coverage describes real task performance as "hit and miss": sometimes errands work well, sometimes they don't, which is an honest description of a still very new tool, not the level of reliability you would expect for delegating sensitive tasks without supervision.
There was also a genuine current of discomfort in public reaction, beyond the technical reviews: the idea of a Meta agent having visibility into travel plans, purchases, and personal errands generated user comments preferring to keep that information out of the company's reach, even in a joking tone. That discomfort does not show up in any benchmark, but it is exactly the kind of market signal that determines whether a product like this gains real adoption beyond initial curiosity.
What does this mean for digital marketing?
For digital marketing, this has two distinct practical implications. The first is the one we were already documenting: if Muse browses and buys on a consumer's behalf using its own built-in browser, your normal conversion tracking probably still works the same as if it were a human, reinforcing that preparing your site for autonomous agents does not require reinventing your measurement from scratch. The second implication is different: any business information your team enters into Muse (client data, strategy, internal figures) is subject to the same conditions just described, protection based on operational policy, not technical impossibility of access, until Confidential VM is available with no confirmed date.
To size this with an illustrative example, not real data but a typical scenario, imagine an agency that starts using Muse for internal administrative tasks, like scheduling meetings or comparing vendors, without first reviewing which data categories get linked to the account according to the actual privacy label. Months later, during a tools audit, the team discovers that calendar information and client contacts passed through a system whose privacy guarantee depends on Meta's internal policy, not a technical barrier, without anyone having made that decision consciously.
At JP Director we treat any tool that handles client information with the same standard, no matter how attractive its functionality is: we review the actual privacy label, not just the launch message, and we wait for verifiable technical guarantees, not just policy promises, before trusting sensitive business information to a third party AI agent.
Frequently Asked Questions
Does Muse share my conversations directly with Meta's advertising systems?
According to Meta, no. The company states that conversations and data generated inside Muse's secure virtual machine are not shared with its advertising systems. However, Muse's App Store privacy label does list "third-party advertising" among the purposes for using data linked to the user, and activity Muse performs on external websites can indirectly influence advertising through that site's normal tracking.
What is Muse Confidential VM and when will it be available?
It is a hardware-encrypted environment with a cryptographic key only the user holds, designed to prevent Meta's own personnel from accessing the data, unlike current protection which depends on operational policy. Meta hired Moxie Marlinspike, Signal's founder, to develop it, but announced it as available "later this year" with no confirmed date as of this publication.
Is Meta's 17.1 billion dollar settlement related to Muse?
Not directly. The settlement, reached roughly two weeks after Muse's launch, resolves claims from 29 state attorneys general regarding child safety related to Meta's platforms in general, not specifically to Muse. However, it is relevant as trust context when evaluating the privacy guarantees the company makes about any of its new products, including Muse.
Should my business avoid using Muse entirely because of these findings?
Not necessarily; it depends on what type of information you plan to trust it with. For low risk administrative tasks, the operational policy based protection that exists today may be acceptable. For sensitive business or client information, the prudent recommendation is to wait until Muse Confidential VM is available with a real technical barrier, or to limit what categories of information you enter until then, rather than assuming the current launch announcement's privacy guarantee covers every use case.
Last updated: September 2026. Muse's privacy policies and feature availability may change; verify the current status directly in Meta's privacy policy and the app's privacy label before making decisions about what information to trust it with.